Historical report: Jinse Finance published this account on November 16, 2026, at 15:47 (UTC+8). EIP-8288 is discussed here as a proposal, not an activated Ethereum upgrade.
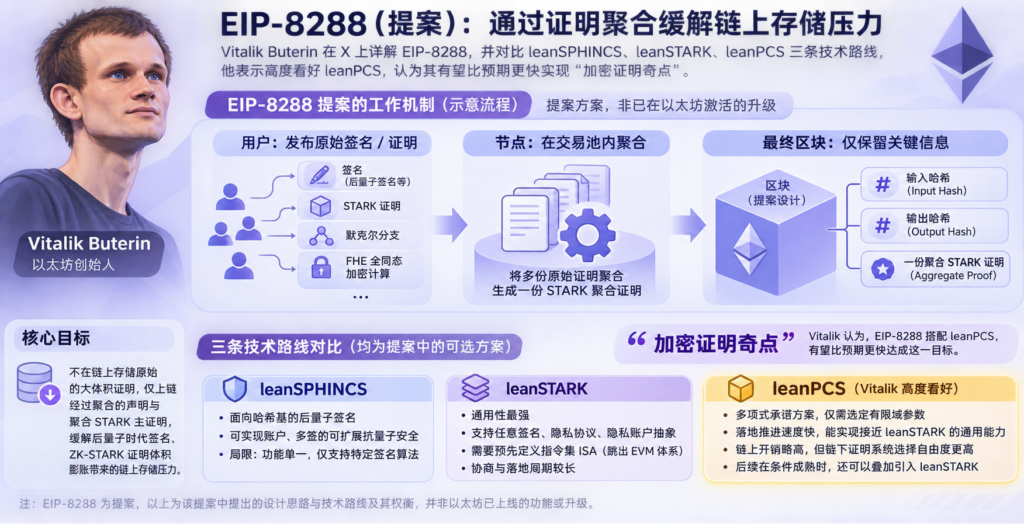
Vitalik Buterin discussed EIP-8288 and three possible technical approaches—leanSPHINCS, leanSTARK and leanPCS—in a post on X. He said he strongly favors leanPCS as a route that could bring what he calls a “cryptographic proof singularity” sooner than expected.
The proposal addresses a storage problem: post-quantum signatures and ZK-STARK proofs can be large, even when the underlying computation needs to be verified only once. The reported design covers tasks such as signature checks, STARK proofs, Merkle branches and fully homomorphic encryption computations. Users would publish the original signatures or proofs; nodes would aggregate them in the transaction pool into a STARK proof. The final block would contain input and output hashes and one aggregate proof, rather than the full original proofs.
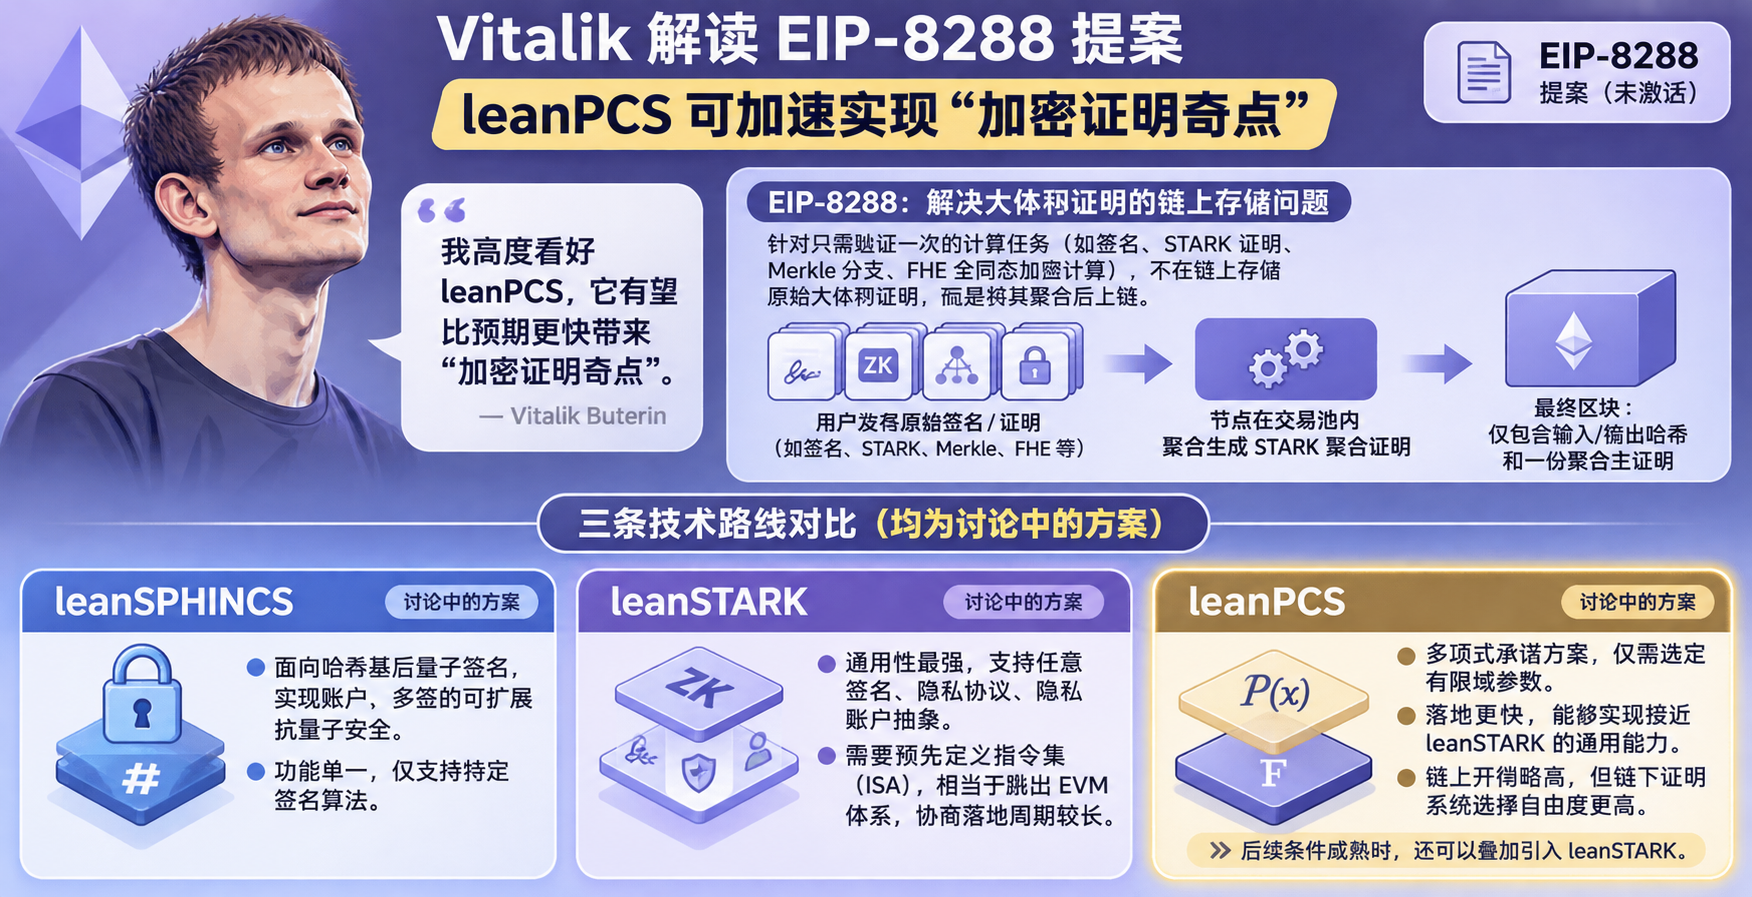
Buterin compared three routes:
- leanSPHINCS would provide scalable, hash-based post-quantum security for accounts and multisignature use, but is limited to a specific signature algorithm.
- leanSTARK would offer broader support, including arbitrary signatures, privacy protocols and private account abstraction. It would require an agreed instruction set outside the EVM framework, making coordination and deployment a longer process.
- leanPCS, a polynomial commitment scheme, would require agreement on finite-field parameters. Buterin described it as faster to advance and close to leanSTARK in generality, with somewhat higher on-chain costs but more freedom in choosing off-chain proving systems. He said leanSTARK could be added later if conditions allow.
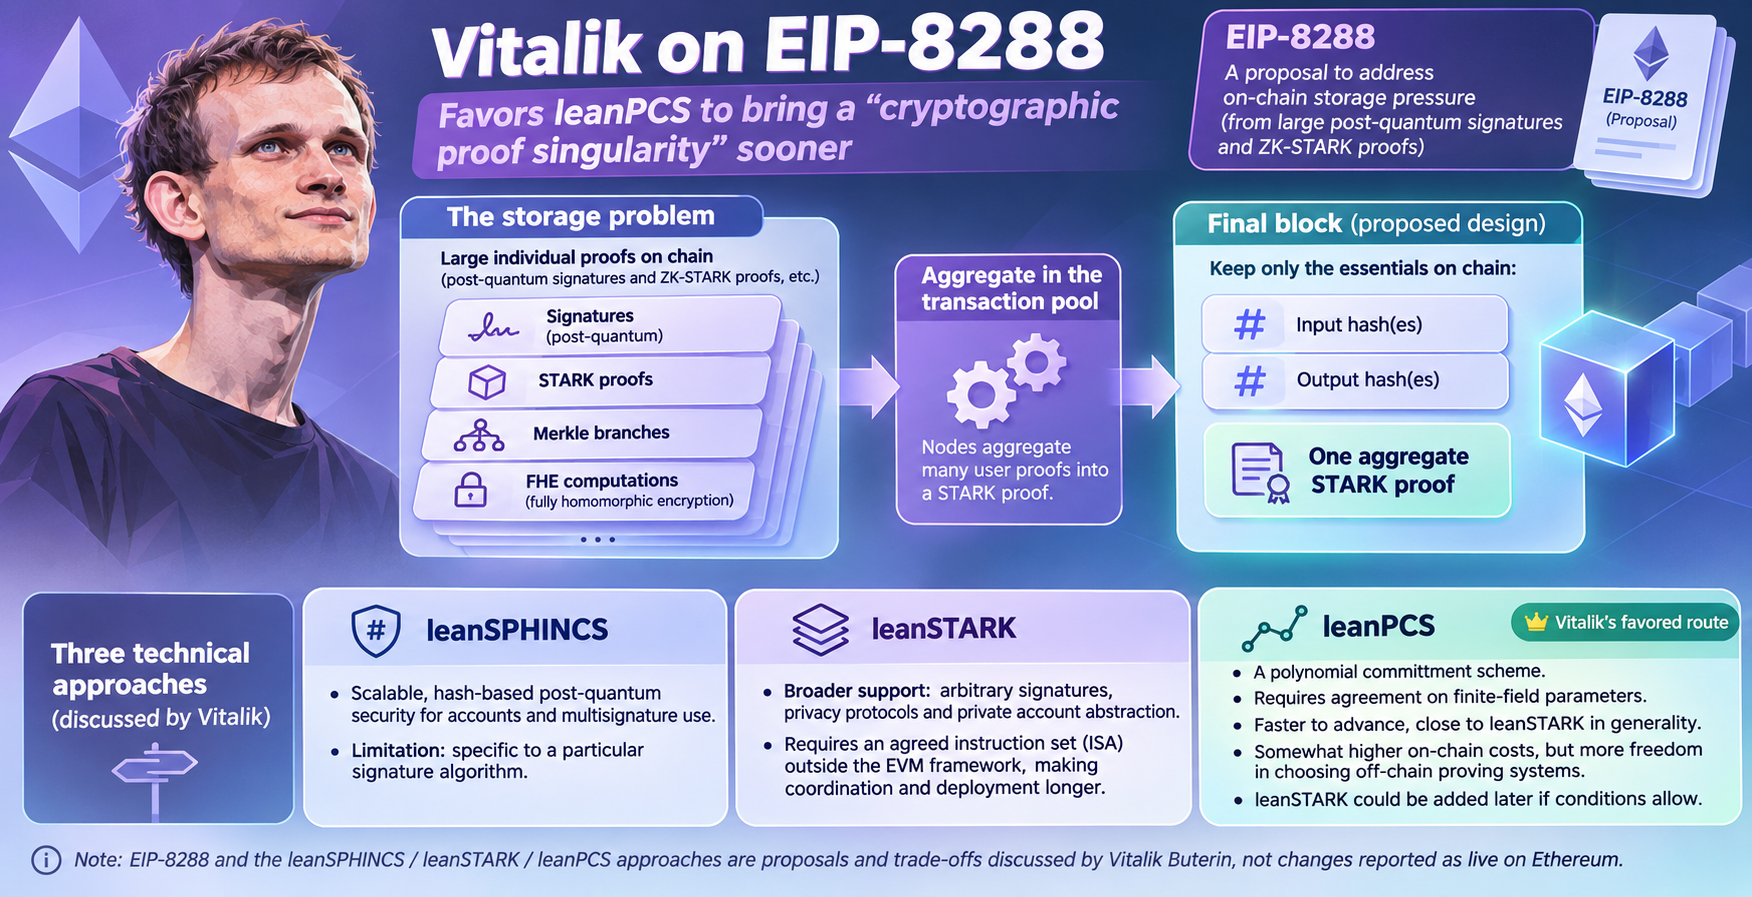
These are proposed approaches and trade-offs, not changes reported as live on Ethereum.
Source: jinse.com.cn (originally published 2026-11-16 15:47 UTC+8)